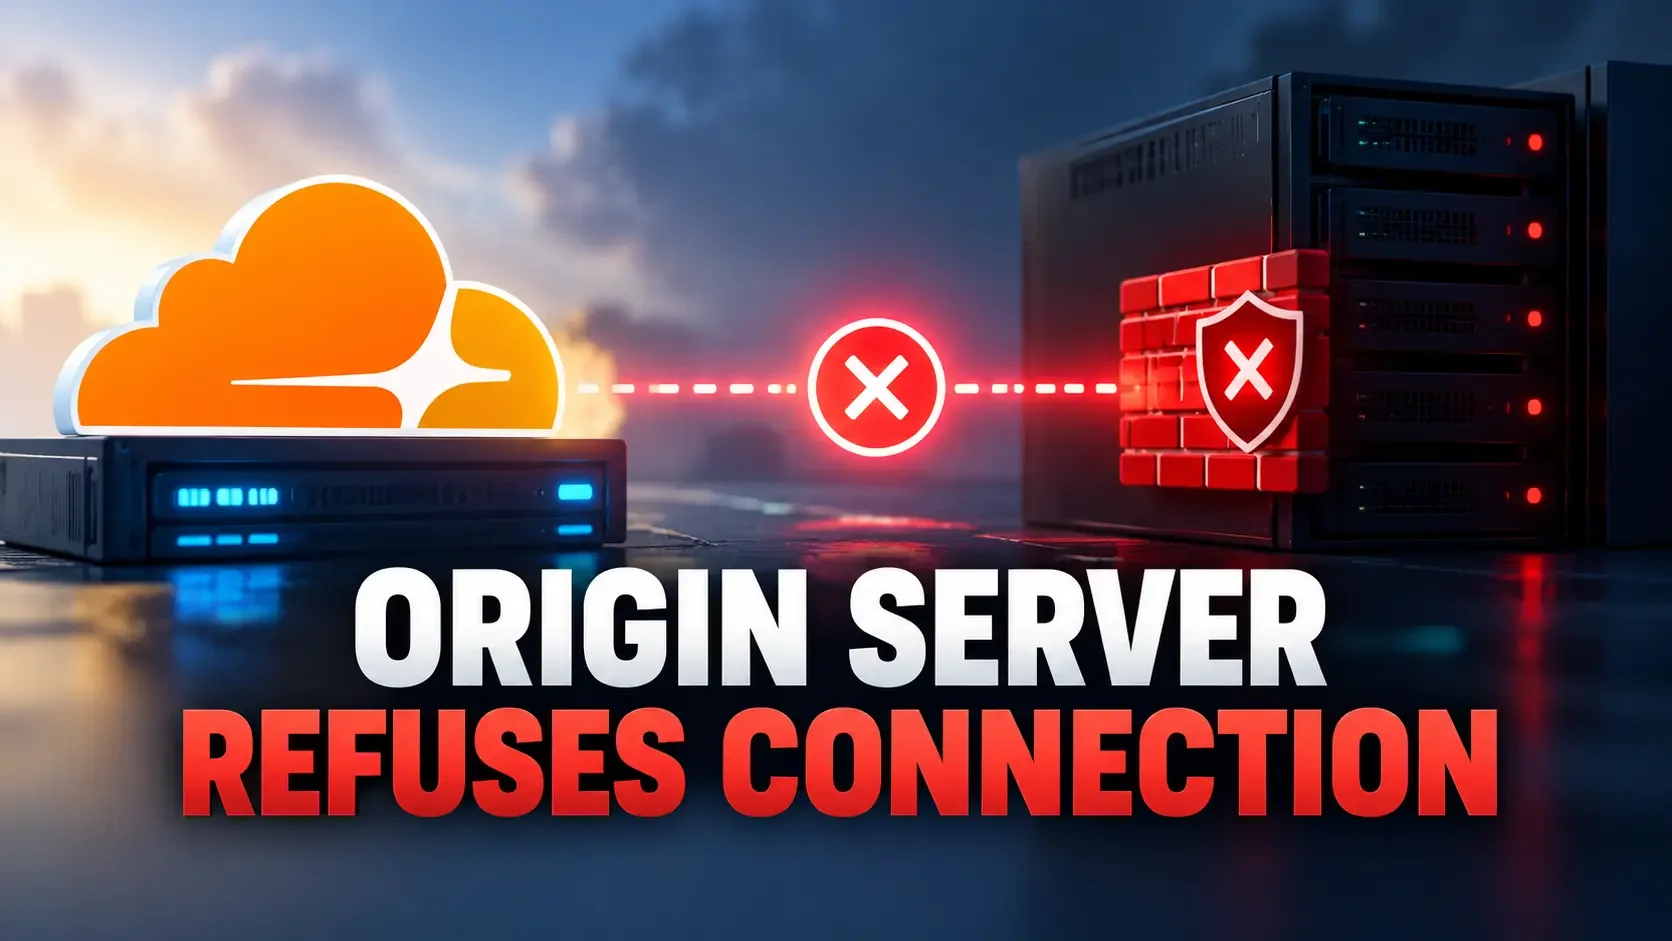
Cloudflare Error 521, commonly displayed as “Web server is down,” occurs when Cloudflare attempts to connect to your website's origin server but the connection is refused. Your hosting account may still be active and the server itself may be running, but Cloudflare can not establish the connection needed to retrieve your website.
The most common causes are a stopped web server application, firewall rules rejecting Cloudflare's IP addresses or a server that is not accepting connections on the required port. Identifying which condition applies is essential because each requires a different correction.
What Causes Cloudflare Error 521?
Error 521 occurs before Cloudflare receives a normal HTTP response from the origin. The connection is rejected rather than successfully established, which distinguishes this error from problems involving page content or application responses.
According to Cloudflare's documentation, an offline web server application and blocked Cloudflare requests are the two primary causes. However, the circumstances in which the error started can help you identify other configuration problems affecting the same connection.
| When Error 521 appears | What may be wrong | Where to investigate |
|---|---|---|
| After restarting or updating the server | Nginx or Apache failed to start | Web server service and error logs |
| After changing firewall rules | Cloudflare IP addresses are blocked | Origin firewall and security software |
| After changing SSL/TLS settings | Required connection port is unavailable | Port 80 or 443 |
| After moving to another hosting provider | Cloudflare points to an old origin | DNS records |
| Only during certain requests | Firewall restrictions or an unhealthy origin backend | Security logs and load balancer |
These circumstances provide a starting point, not a confirmed diagnosis. For example, an error appearing after a hosting migration may result from an outdated DNS record or a firewall configuration that was not transferred correctly.
Check Whether the Web Server Is Running
A common mistake is assuming that an active hosting account means the website's web server is working. The operating system can remain available while Nginx, Apache or another HTTP service has stopped accepting connections.
If you manage a VPS, connect through SSH and inspect the web server service. For Nginx, run:
sudo systemctl status nginx
For Apache on Ubuntu or Debian, use:
sudo systemctl status apache2
If the service reports inactive or failed, examine its logs to determine why it stopped. A recent configuration change, failed update or service crash may explain why Cloudflare suddenly started returning Error 521.
For an Nginx server, you can test the configuration before attempting a restart:
sudo nginx -t
If the command reports a configuration error, correct it before restarting Nginx. If the configuration is valid and the service has stopped, restart it and confirm that its status changes to active (running).
What if the service is already running?
A running service does not guarantee that it is listening on the correct network port. Check the active TCP listeners using:
sudo ss -lntp
Look for port 80 or 443, depending on your origin configuration. If the required port is missing, examine the web server's listener configuration.
Also check the listening address. A service bound only to 127.0.0.1 may accept local requests while refusing connections arriving through the server's public network interface.
If the correct port is listening on an appropriate interface, the next investigation should focus on whether Cloudflare's traffic can reach it.
Check If Your Firewall Blocks Cloudflare
Cloudflare connects to proxied websites using its own IP addresses. This means your origin firewall sees connections from Cloudflare rather than directly from every individual visitor.
Some security systems interpret repeated connections from shared IP addresses as suspicious activity. If the firewall blocks or rate-limits those addresses, legitimate Cloudflare requests may be refused.
This problem often appears after installing new security software, tightening firewall restrictions or enabling automatic IP blocking.
Identify the blocking rule
Examine the security logs for rejected connections around the time Error 521 occurred. Depending on your hosting environment, these records may be available through a server firewall, cloud security group, hosting control panel or security application.
Compare the rejected source addresses with Cloudflare's published IP ranges. If the blocked traffic originates from Cloudflare, identify whether an explicit firewall rule, automatic ban or rate limit is responsible.
Cloudflare maintains its current IP ranges at cloudflare.com/ips/. Use that official list instead of relying on addresses copied from outdated troubleshooting guides.
Correct the restriction
Allow the necessary Cloudflare IP ranges through the firewall protecting your origin. Review both IPv4 and IPv6 rules where applicable, especially if the server uses different security policies for each address family.
If an automatic security system caused the block, adjust the responsible rule so legitimate Cloudflare connections are not rejected again. Simply removing a temporary ban may not provide a lasting solution if the same rule immediately blocks the addresses again.
Do not disable your entire server firewall to solve Error 521. Make the necessary changes to the specific restriction while keeping other security protections active.
An incomplete Cloudflare IP allowlist can also explain intermittent failures. If only some Cloudflare source addresses are permitted, requests may succeed through one connection and fail through another.
Check the Origin IP and Required Port
If the web server is running and no Cloudflare-related firewall block is found, verify that Cloudflare is connecting to the correct destination.
This check is particularly important when Error 521 begins after a hosting migration, DNS update or change to your SSL/TLS configuration.
Confirm the origin IP address
In your Cloudflare dashboard, open DNS → Records and locate the record for the affected hostname.
Check the configured A or AAAA address against the IP address currently assigned to your origin server. If the hostname uses a CNAME record, verify that its target resolves to the intended origin service.
For example, imagine that your website recently moved to a new VPS but Cloudflare still points to the previous server. If the old destination refuses the incoming connection, Cloudflare may return Error 521 even though the new server is working normally.
Update an incorrect record only after confirming the correct destination with your hosting provider. If several origin addresses are configured, verify each one rather than assuming that all records point to healthy servers.
Check the connection port
Cloudflare must connect to a port supported by your origin configuration. For websites using the standard HTTP and HTTPS ports, the relevant requirement depends on the SSL/TLS encryption mode.
| SSL/TLS mode | Origin connection requirement |
|---|---|
| Flexible | HTTP on port 80 |
| Full | HTTPS on port 443 for HTTPS requests |
| Full (strict) | HTTPS on port 443 for HTTPS requests, with valid certificate requirements |
Suppose Error 521 begins immediately after changing Cloudflare from Flexible to Full. If the origin was previously accepting only HTTP connections on port 80, Cloudflare may now encounter a refused connection when attempting HTTPS on port 443.
The appropriate correction is to configure the origin to accept the required HTTPS connection and ensure the firewall permits it. Changing encryption modes repeatedly without identifying the refused port can conceal the actual configuration problem.
A connection refusal should also be distinguished from a failed TLS handshake or invalid certificate. Those conditions can produce different Cloudflare errors, including 525 and 526.
Test the Origin Connection Directly
When the previous checks do not identify the cause, a direct connection test can provide evidence about the origin's behaviour.
For a server you administer, use curl with the --resolve option to connect to the origin IP while preserving the website's hostname.
curl -Iv --resolve example.com:443:203.0.113.10 https://example.com/
Replace example.com with your actual hostname and 203.0.113.10 with your origin IP address. The example assumes that your website should accept HTTPS connections on port 443.
This command bypasses normal DNS resolution for the specified hostname and directs the request to the chosen origin. It helps determine whether that destination accepts the connection without requiring you to modify public DNS records.
Interpret the result
The result should guide the next investigation rather than being treated as a complete diagnosis.
| Result | What it indicates | What to do |
|---|---|---|
| Connection refused | The destination rejected the TCP connection | Inspect the web server listener and firewall |
| Connection timed out | The connection could not complete | Investigate network reachability and filtering |
| HTTP response received | The server accepted the connection | Examine restrictions affecting Cloudflare specifically |
| Certificate verification failed | The connection progressed to TLS verification | Investigate certificate trust and configuration |
A successful direct connection does not prove that Cloudflare can reach the server. Your origin may accept traffic from your testing device while refusing requests from Cloudflare's IP addresses.
Likewise, some websites intentionally restrict direct origin access to prevent visitors from bypassing Cloudflare's protection. In that configuration, a rejected connection from your computer may be expected.
The most useful evidence comes from combining the test result with the origin's security logs. If the connection is refused before reaching Nginx or Apache, the normal HTTP access log may contain no record of the attempt.
When Error 521 Affects Only Some Requests
An intermittent Error 521 can indicate that the origin is accepting certain connections while refusing others. This is especially important for websites using multiple backend servers or load balancers.
For example, a load balancer may distribute requests between two origin servers. If one server accepts connections while the other has a stopped web service, visitors may receive alternating successful responses and Error 521 pages.
Check the health and listener configuration of each backend rather than investigating only the server that appears operational. Compare the times of failed requests with service interruptions, deployment events and load balancer records.
If your website uses a single origin, examine whether the web server is restarting unexpectedly or whether security restrictions activate during traffic spikes. These patterns can explain why the connection appears healthy during testing but fails again later.
If Cloudflare Connections Are Still Refused
When the web server is listening on the correct port, DNS points to the intended origin and the firewall appears properly configured, investigate any additional network components between Cloudflare and the server.
A hosting-provider firewall, reverse proxy or load balancer may reject the connection before it reaches the web server. These failures may not appear in ordinary website access logs, so the relevant network or infrastructure logs become important.
If your hosting provider manages those components, provide the affected URL, the Error 521 message, the approximate failure time with time zone and the Cloudflare Ray ID when available. Include the origin IP, expected connection port and any relevant test results.
Ask the provider to determine where connections from Cloudflare are being refused. This directs the investigation toward the actual connection failure instead of treating Error 521 as a general website outage.
After correcting the responsible component, access the website through its normal Cloudflare-proxied hostname and confirm that requests complete successfully. For intermittent failures, verify that the issue no longer occurs across the affected origin servers or connection paths.